Cybersecurity Lead Generation: How to Build a Pipeline That Doesn’t Depend on Referrals
Most cybersecurity firms will tell you their best clients came from referrals. That’s usually true. It’s also a problem.
Referrals are real revenue, but they’re not a cybersecurity lead generation strategy. They can’t be measured, forecasted, or replicated. They reward the relationships you built two or three years ago, not the pipeline decisions you’re making today. And when a quiet quarter hits, no warm intros, no anchor client renewals, just silence, there’s nothing to pull from.
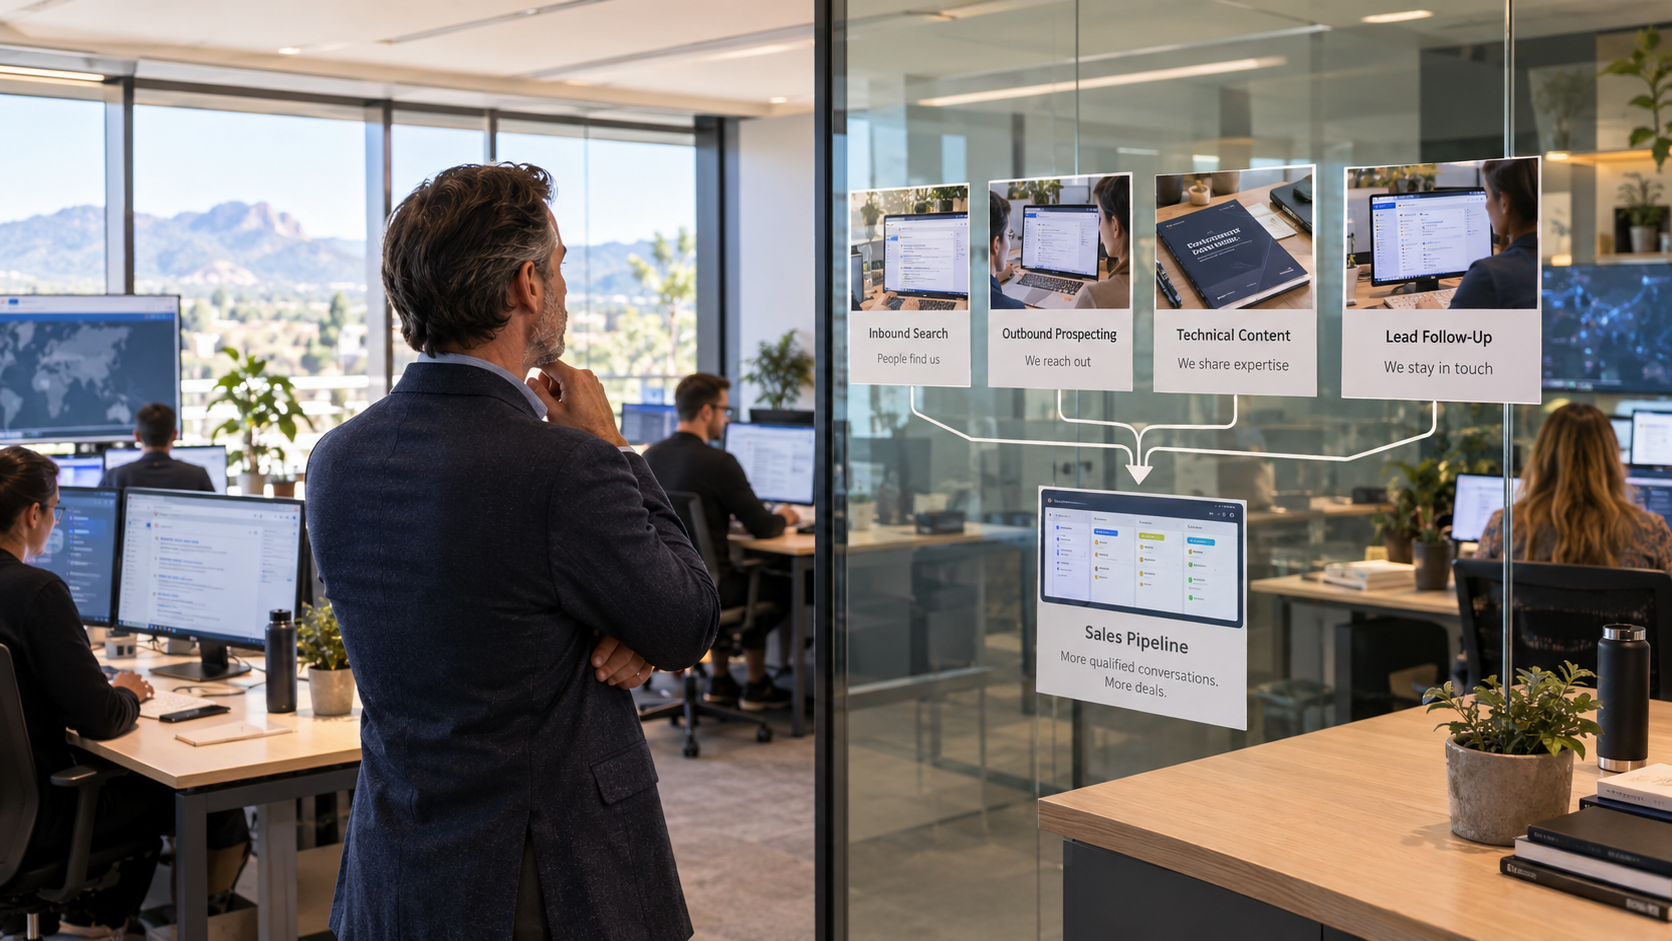
This post lays out a four-layer system for building predictable pipeline as a cybersecurity firm: inbound SEO, outbound prospecting, content that actually builds trust, and the post-lead process most firms skip entirely. None of it replaces referrals. It runs alongside them, so you’re not dependent on them.
Observations in this post reflect our experience working with cybersecurity firms. Results vary based on firm size, market, service type, and execution.
Why Referrals Aren’t a Lead Generation Strategy (They’re a Revenue Risk)
There’s nothing wrong with referrals. The problem is treating them as a pipeline system when they’re actually a lagging indicator of relationships you built years ago.
Referrals have several structural problems as a primary growth channel:
• They can’t be forecasted. You can’t build a quarterly revenue model on “someone might introduce us to someone.”
• They don’t scale. Your referral rate is capped by the size of your existing client base and their willingness to refer, neither of which you control.
• They concentrate risk. If two or three anchor clients represent most of your referral flow, a single churn event can quietly dry up your pipeline for the next six months.
• They’re invisible until they arrive. There’s no early warning system. A referral either shows up or it doesn’t.
The goal isn’t to stop earning referrals. It’s to build a system that generates qualified conversations whether or not a referral comes in this quarter.
Layer 1, Inbound SEO: Get Found When Buyers Are Actively Searching
Security buyers search. They search when they’ve had an incident, when a compliance deadline appears on the calendar, when their insurance carrier asks for a risk assessment, and when they’ve finally decided to stop patching the problem internally. When they search, you either show up or you don’t.
Target Problem-Aware Keywords, Not Just Service Keywords
Most cybersecurity firms optimize for their own service names, “managed security services,” “penetration testing,” “SOC as a service.” These terms have search volume, but buyers using them are still in the awareness phase. They’re not ready to evaluate vendors yet.
The higher-intent searches look like this:
• “CMMC compliance consultant [state]”
• “how to pass a SOC 2 Type II audit”
• “managed SIEM pricing for mid-market”
• “what does a MSSP actually cover”
• “do I need a vCISO or a full-time CISO”
Buyers searching these phrases are mid-evaluation. They’ve already decided they have a problem, now they’re deciding who to trust with it. Show up here with something genuinely useful and you’re in the conversation before competitors have a chance.
Technical Authority Content Beats Generic Blog Posts
Security buyers are sophisticated. Many of them have technical backgrounds. They will read your content before they talk to you, and if it’s shallow, they’ll decide you’re not worth the conversation.
A post titled “5 Reasons Cybersecurity Matters for Your Business” is noise. A post that walks through how CMMC 2.0 Level 2 affects a specific subset of defense contractors, with clear explanations of what’s required and what the assessment process actually looks like, earns credibility before a sales conversation starts.
Depth and specificity are the differentiators. Generic content signals a generic firm. For more on how to build this kind of content systematically, see our guide to building a cybersecurity content marketing system.
Layer 2, Outbound Prospecting: Reach Buyers Before They Start Searching
Inbound captures buyers who already know they have a problem. Outbound lets you reach the ones who have the problem but haven’t started looking yet, or who are working with a vendor they’ve quietly outgrown.
Define the ICP Before You Write a Single Email
The most common outbound mistake in cybersecurity marketing is going broad. “Any company with 50-500 employees that handles sensitive data” is not an ICP. It’s a list. And a list without real qualification produces low reply rates and wasted cycles.
A tighter ICP for a cybersecurity firm might look like:
• Defense contractors in CMMC scope with 50-200 employees
• Financial services firms with a recent SOC audit gap
• Healthcare organizations approaching their HIPAA risk assessment cycle
• PE-backed companies in the 30-90 days post-acquisition window (integration risk is high, security posture is often unknown)
Trigger-based targeting is more effective than static lists. Compliance deadlines, regulatory changes, funding announcements, and breach news in a prospect’s sector are all signals that security is on the table right now.
Build Sequences That Lead With Insight, Not Pitch
Security buyers are bombarded with cold outreach from vendors claiming to “reduce risk” and “protect your business.” The fastest way to differentiate is to lead with something genuinely useful: a relevant regulatory update, a specific observation about their tech stack, a framework for thinking about a decision they’re facing.
A useful test for any outbound email: if you removed all mention of your firm, would the recipient still find it worth reading? If not, it’s a pitch, and it reads like one.
LinkedIn is the right primary channel for reaching CISOs, IT directors, and compliance leads. In our experience, decision-makers in security tend to be active on LinkedIn, and in many cases are more likely to engage with a thoughtful message there than a cold email. For a more detailed breakdown of building a full outbound system, see our post on B2B outbound prospecting.
Layer 3, Content as Trust Infrastructure (Not Just Traffic)
Most firms treat content as a traffic play. Get ranked, get visits, hope some of them convert. That’s not wrong, but it undersells what content actually does for a cybersecurity firm.
Security buyers don’t trust marketing. They trust specificity, credentials, and proof. Content is where you demonstrate all three before a prospect ever talks to you.
The content that actually moves security buyers:
• Technical deep-dives, walkthroughs of specific frameworks, audit prep guides, implementation breakdowns. These signal that you know what you’re talking about at a practitioner level.
• Compliance checklists, practical tools that a buyer can use right now. These earn goodwill and keep your firm top of mind when they’re ready to engage.
• Anonymized incident or assessment case studies, what went wrong, what you found, how you fixed it. These are the highest-trust content type in the category and the hardest to fake.
In our experience, one strong technical piece per quarter, published consistently, typically outperforms eight shallow blog posts. Content is a trust infrastructure investment. It compounds. A post that earns a ranking today is still converting readers two years from now.
If you run a vCISO practice, this dynamic is even more pronounced, your content is often the first substantive thing a prospect sees from you. For a deeper look at vCISO-specific marketing, see our guide on vCISO marketing.
Layer 4, The Part Most Cybersecurity Firms Skip: What Happens After the Lead Comes In
Here’s where most cybersecurity marketing systems leak. Not at the top of the funnel, at the bottom.
A prospect fills out your contact form, downloads a compliance checklist, or replies to a LinkedIn message. What happens next? In most firms: a delayed response, a generic acknowledgment, and a follow-up cadence that goes quiet after two touchpoints.
That’s where the pipeline dies, not in your marketing, but in your follow-up.
Speed-to-Lead Matters More Than Most Firms Think
Security deals are high-trust, long-cycle purchases. It’s tempting to assume that a 48-hour response is fine because “no one expects instant replies in enterprise B2B.” That assumption is expensive.
The firm that responds first and with something substantive earns the evaluation slot. Security buyers are often evaluating two or three vendors simultaneously. The first credible response shapes how every subsequent conversation is judged.
Build a Follow-Up System for the Long Cycle
In our experience, many security deals close in 60 to 180 days, though this varies considerably by firm size, service type, and buyer. Even so, in our experience working with cybersecurity firms, we frequently see follow-up stopping after two weeks, and the lead going cold from there. That gap, weeks three through twenty-four, is where deals are lost to competitors who stayed in the conversation.
A functioning follow-up system for cybersecurity looks like:
• An immediate, specific response to the initial inquiry (not a templated acknowledgment)
• A structured nurture sequence for prospects who aren’t ready to engage yet, one touchpoint per month with relevant content or regulatory updates
• A clear lead routing process: who owns the inquiry, what’s the handoff to a technical resource if needed, and what’s the expected response time
This is the most consistently neglected part of a cybersecurity marketing system. Fixing it doesn’t require more traffic or a bigger ad budget, it requires process. For a practical framework, see our post on building a B2B lead follow-up system.
A Simple Cybersecurity Pipeline Audit: 5 Questions
Before investing in more traffic or more outbound volume, use these five questions to locate where your current pipeline is leaking:
1. If referrals stopped tomorrow, would your pipeline survive the next quarter? If the honest answer is no, the system doesn’t exist yet, it needs to be built.
2. Are you showing up in search results for the problems your buyers are Googling right now? Not your service names, their problems, their compliance frameworks, their decision questions.
3. Does your outbound target a specific ICP segment, or a broad list? Specificity drives reply rates. Broad targeting drives unsubscribes.
4. What does your content signal about your technical depth? Would a CISO read it and find something useful, or would they close the tab in ten seconds?
5. What happens in the first 24 hours after a lead submits? Is there a process, or does it depend on whoever happens to see the email first?
In our work with cybersecurity clients, we most often find the leak in question four or five. The top of the funnel is fine. The post-lead process is broken.
Building a Cybersecurity Pipeline That Runs Without You
Effective cybersecurity lead generation isn’t about running more ads or writing more blog posts. It’s about building a system where each layer, inbound, outbound, content, and follow-up, works in sequence, and no single layer is carrying the whole load.
Referrals will still come in. When they do, they’ll be a bonus rather than a lifeline. That’s a much better position to operate from.
If your cybersecurity firm is ready to stop depending on referrals and build a real pipeline system, we’d like to talk. Apply to work with Timberbrook and we’ll take a look at where your current pipeline is leaking and what it would take to fix it.
Written by the team at Timberbrook Marketing.